

[Jan 06, 2022] Lesson Brilliant PDF for the NSE7_SDW-6.4 Tests Free Updated Today
Get New 2022 Valid Practice NSE 7 Network Security Architect NSE7_SDW-6.4 Q&A - Testing Engine
Fortinet NSE7_SDW-6.4 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
NEW QUESTION 16
Refer to exhibits.
Exhibit A.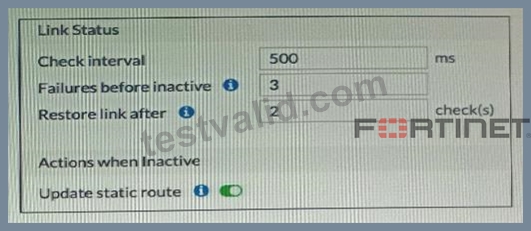
Exhibit B.
Exhibit A shows the SD-WAN performance SLA and exhibit B shows the SO-WAN interface and the static routes configuration.
Port1 and port2 are member interfaces of the SD-WAN, and port2 becomes a dead member after reaching the failure thresholds Which statement about the dead member is correct?
- A. Dead members require manual administrator access to bring them back alive
- B. SD-WAN interface becomes disabled and port1 becomes the WAN interface
- C. Port2 might become alive when a single response is received from an SLA server
- D. Subnets 100 .64-1.0/23 and 172 . 20 . 0. 0/16 are reachable only through port1
Answer: B
NEW QUESTION 17
Refer to the exhibit.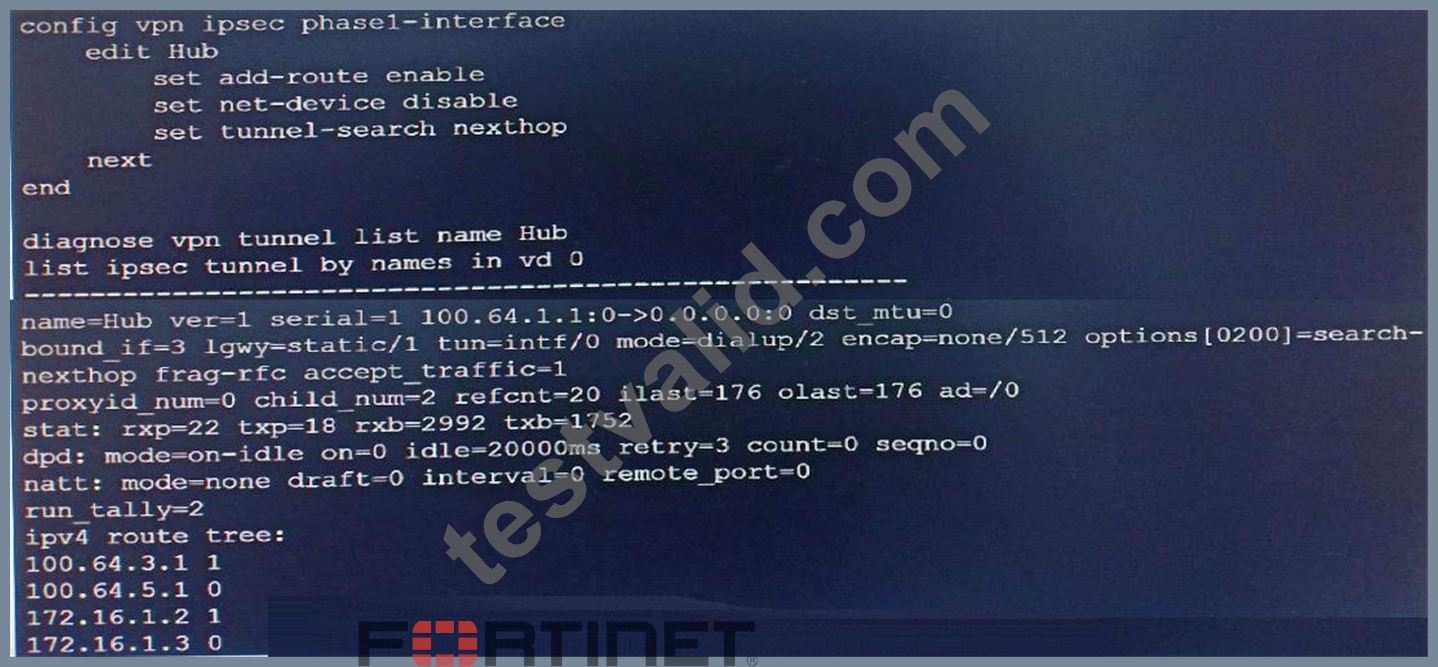
Which two statements about the status of the VPN tunnel are true? <Choose two )
- A. There are separate virtual interfaces for each dial-up client
- B. VPN static routes are prevented from populating the FortiGate routing table
- C. FortiGate created a single IPsec virtual interface that is shared by all clients
- D. 100.64.3.1 is one of the remote IP address that comes through index interlace 1.
Answer: A
NEW QUESTION 18
Which two reasons make forward error correction (FEC) ideal to enable in a phase one VPN interface? (Choose two )
- A. FEC is useful to increase speed at which traffic is routed through IPsec tunnels.
- B. FEC improves reliability which overcomes adverse WAN conditions such as noisy links.
- C. FEC transmits additional packets as redundant data to the remote device.
- D. FEC transmits the original payload in full to recover the error in transmission.
- E. FEC reduces the stress on the remote device jitter buffer to reconstruct packet loss
Answer: B,C
NEW QUESTION 19
Refer to the exhibit.
FortiGate has multiple dial-up VPN interfaces incoming on portl that match only FIRSTJVPN.
Which two configuration changes must be made to both IPsec
VPN interfaces to allow incoming connections to match all possible IPsec dial-up interfaces? (Choose two )
- A. Use unique Diffie Hellman groups on each VPN interface
- B. Configure the IKE mode to be aggressive mode
- C. Use different proposals are used between the interfaces.
- D. Configure a unique peer ID for each dial-up VPN interface
Answer: B,D
NEW QUESTION 20
Refer to the exhibit.
What must you configure to enable ADVPN?
- A. The protected subnets should be set to address object to all (0.0.0.0/0).
- B. On the hub VPN, only the device needs additional phase one settings.
- C. ADVPN should only be enabled on unmanaged FortiGate devices.
- D. Each VPN device has a unique pre-shared key configured separately on phase one.
Answer: D
Explanation:
Explanation/Reference:
NEW QUESTION 21
Which diagnostic command you can use to show interface-specific SLA logs for the last 10 minutes?
- A. diagnose sys virtual-wan-link sla-log
- B. diagnose sys virtual-wan-link log
- C. diagnose sys virtual-wan-link intf-sla-log
- D. diagnose sys virtual-wan-link health-check
Answer: A
Explanation:
Explanation/Reference: https://docs.fortinet.com/document/fortigate/6.2.0/cookbook/943037/sla-logging
NEW QUESTION 22
Refer to the exhibit.
Multiple IPsec VPNs are formed between two hub-and-spokes groups, and site-to-site between Hub 1 and Hub 2 The administrator configured ADVPN on the dual regions topology
Which two statements are correct if a user in Toronto sends traffic to London? (Choose two )
- A. The first packets from Toronto to London are routed through Hub 1 then to Hub 2.
- B. Traffic from Toronto to London triggers the dynamic negotiation of a direct site-to-site VPN
- C. London generates an IKE information message that contains the Toronto public IP address
- D. Toronto needs to establish a site-to-site tunnel with Hub 2 to bypass Hub 1.
Answer: B,D
NEW QUESTION 23
Refer to exhibits.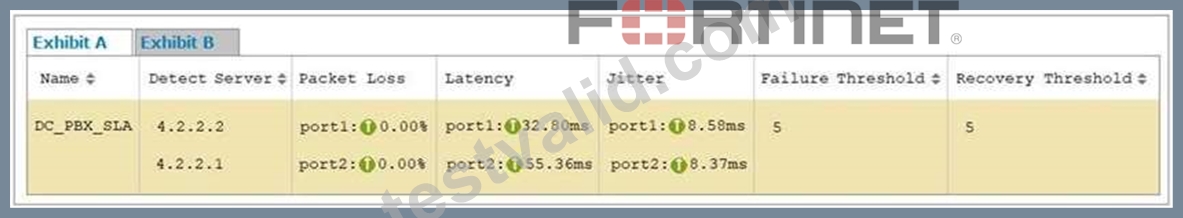

Exhibit A shows the performance SLA exhibit B shows the SD-WAN diagnostics output.
Based on the exhibits, which statement is correct?
- A. Both SD-WAN member interfaces have used separate SLA targets.
- B. Port1 became dead because no traffic was offload through the egress of port1.
- C. The SLA state of port1 is dead after five unanswered requests by the SLA servers.
- D. SD-WAN member interfaces are affected by the SLA state of the inactive interface.
Answer: C
NEW QUESTION 24
Refer to the exhibit.
What must you configure to enable ADVPN?
- A. ADVPN should only be enabled on unmanaged FortiGate devices.
- B. The protected subnets should be set to address object to all (0.0 .0. o/o).
- C. Each VPN device has a unique pre-shared key configured separately on phase one
- D. On the hub VPN, only the device needs additional phase one sett
Answer: C
NEW QUESTION 25
An administrator is troubleshooting VoIP quality issues that occur when calling external phone numbers. The SD-WAN interface on the edge FortiGate is configured with the default settings, and is using two upstream links. One link has random jitter and latency issues, and is based on a wireless connection.
Which two actions must the administrator apply simultaneously on the edge FortiGate to improve VoIP quality using SD-WAN rules? (Choose two.)
- A. Select the corresponding SD-WAN balancing strategy in the SD-WAN rule.
- B. Use the performance SLA targets to detect latency and jitter instantly.
- C. Configure an SD-WAN rule to load balance all traffic without VoIP.
- D. Place the troublesome link at the top of the interface preference list.
- E. Choose the suitable interface based on the interface cost and weight.
Answer: A,B
NEW QUESTION 26
Refer to the exhibit.
Which statement about the trace evaluation by FomGate is true?
- A. Packets exceeding the configured maximum concurrent connection limit are denied by the per-IP shaper.
- B. Packets exceeding the configured concurrent connection limit are dropped based on tfte priority configuration.
- C. The packet exceeded the configured bandwidth and was dropped based on the priority configuration
- D. The packet exceeded the configured maximum bandwidth and was dropped by the shared shaper.
Answer: B
NEW QUESTION 27
Which statement defines how a per-IP traffic shaper of 10 Mbps is applied to the entire network?
- A. The 10 Mbps bandwidth is shared equally among the IP addresses.
- B. FortiGate allocates each IP address a maximum 10 Mbps of bandwidth.
- C. A single user uses the allocated bandwidth divided by total number of users.
- D. Each IP is guaranteed a minimum 10 Mbps of bandwidth.
Answer: B
Explanation:
Explanation/Reference:
https://docs.fortinet.com/document/fortigate/6.2.0/cookbook/885253/per-ip-traffic-shaper
NEW QUESTION 28
Which two statements describe how IPsec phase 1 main mode is different from aggressive mode when performing IKE negotiation? (Choose two )
- A. A peer ID is included in the first packet from the initiator, along with suggested security policies.
- B. The use of Diffie Hellman keys is limited by the responder and needs initiator acceptance.
- C. A total of six packets are exchanged between an initiator and a responder instead of three packets.
- D. XAuth is enabled as an additional level of authentication, which requires a username and password.
Answer: C,D
NEW QUESTION 29
Refer to exhibits.
Exhibit A.
Exhibit B.
Exhibit A shows the source NAT global setting and exhibit B shows the routing table on FortiGate Based on the exhibits, which two statements about increasing the port2 interface priority to 20 are true? (Choose two )
- A. All the existing sessions will continue to use port2 and new sessions will use port1
- B. All the existing sessions with no SNAT will start using port1 as the outgoing interface instead of port2
- C. All the existing sessions will be blocked from using port1 and port2
- D. All the existing sessions using SNAT will start using port1 as the outgoing interface instead of port2.
Answer: B,D
NEW QUESTION 30
In the default SD-WAN minimum configuration, which two statements are correct when traffic matches the default implicit SD-WAN rule? (Choose two )
- A. The FIB lookup resolved interface was the SD-WAN member interface
- B. Traffic has matched none of the FortiGate policy routes
- C. An absolute SD-WAN rule was defined and matched traffic
- D. Matched traffic failed RPF and was caught by the rule.
Answer: B,C
NEW QUESTION 31
Which two statements reflect the benefits of implementing the ADVPN solution to replace conventional VPN topologies? (Choose two )
- A. It creates redundant tunnels between hub-and-spokes, in case failure takes place on the primary links.
- B. It ensures that spoke-to-spoke traffic no longer needs to flow through the tunnels through the hub.
- C. It dynamically assigns cost and weight between the hub and the spokes, based on the physical distance.
- D. It provides direct connectivity between all sites by creating on-demand tunnels between spokes.
Answer: B,D
NEW QUESTION 32
Refer to exhibits.

Exhibit A shows the SD-WAN rules and exhibit B shows the traffic logs. The SD-WAN traffic logs reflect how FortiGate processed traffic.
Which two statements about how the configured SD-WAN rules are processing traffic are true? (Choose two.)
- A. The initial session of an application goes through a learning phase in order to apply the correct rule.
- B. The implicit rule overrides all other rules because parameters widely cover sources and destinations.
- C. SD-WAN rules are evaluated in the same way as firewall policies: from top to bottom.
- D. The All_Access_Rules rule load balances Vimeo application traffic among SD-WAN member interfaces.
Answer: B,C
NEW QUESTION 33
Refer to exhibits.

Exhibit A shows the firewall policy and exhibit B shows the traffic shaping policy.
The traffic shaping policy is being applied to all outbound traffic; however, inbound traffic is not being evaluated by the shaping policy.
Based on the exhibits, what configuration change must be made in which policy so that traffic shaping can be applied to inbound traffic?
- A. A new firewall policy must be created and SD-WAN must be selected as the incoming interface.
- B. The guaranteed-10mbps option must be selected as the reverse shaper option.
- C. The guaranteed-10mbps option must be selected as the per-IP shaper option
- D. The reverse shaper option must be enabled and a traffic shaper must be selected
Answer: B
NEW QUESTION 34
Which diagnostic command can you use to show the SD-WAN rules interface information and state?
- A. diagnose sys virtual-wan-link route-tag-list
- B. diagnose sys virtual-wan-link neighbor.
- C. diagnose sys virtual-wan-link member.
- D. diagnose sys virtual-wan-link service
Answer: B
NEW QUESTION 35
Which statement is correct about the SD-WAN and ADVPN?
- A. Spoke support dynamic VPN as a static interface.
- B. ADVPN interface can be a member of SD-WAN interface.
- C. Dynamic VPN is not supported as an SD-Wan interface.
- D. Hub FortiGate is limited to use ADVPN as SD-WAN member interface.
Answer: B
NEW QUESTION 36
Which statement reflects how BGP tags work with SD-WAN rules?
- A. BGP tags match the SD-WAN rule based on the order that these rules were installed.
- B. VPN topologies are formed using only BGP dynamic routing with SD-WAN
- C. Route tags are used for a BGP community and the SD-WAN rules are assigned the same tag
- D. BGP tags require that the adding of static routes be enabled on all ADVPN interfaces
Answer: B
NEW QUESTION 37
......
NSE7_SDW-6.4 Dumps PDF - 100% Passing Guarantee: https://www.testvalid.com/NSE7_SDW-6.4-exam-collection.html
Latest NSE7_SDW-6.4 PDF Dumps & Real Tests Free Updated Today: https://drive.google.com/open?id=1ZPUPjrx8SX4DZzhAlkTVe0PcaiWqOfvI