

Guaranteed Success in Microsoft 365 MS-500 Exam Dumps
Microsoft MS-500 Daily Practice Exam New 2021 Updated 231 Questions
MS-500 Exam topics
Candidates must know the exam topics before they start of preparation. Because it will really help them in hitting the core. Our MS-500 dumps will include the following topics:
- Implement and manage information protection 15-20%
- Implement and manage threat protection 20-25%
- Implement and manage identity and access 30-35%
- Manage governance and compliance features in Microsoft 365 25-30%
NEW QUESTION 18
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription that contains the users shown in the following table.
You discover that all the users in the subscription can access Compliance Manager reports.
The Compliance Manager Reader role is not assigned to any users.
You need to recommend a solution to prevent a user named User5 from accessing the Compliance Manager reports.
Solution: You recommend modifying the licenses assigned to User5.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION 19
You have a Microsoft 365 subscription that uses a default name of litwareinc.com.
You configure the Sharing settings in Microsoft OneDrive as shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.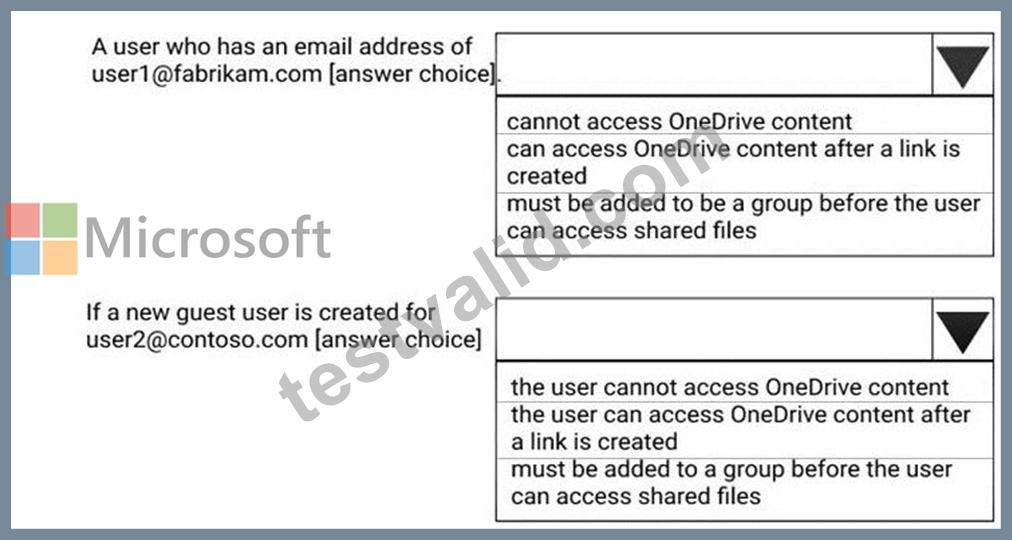
Answer:
Explanation: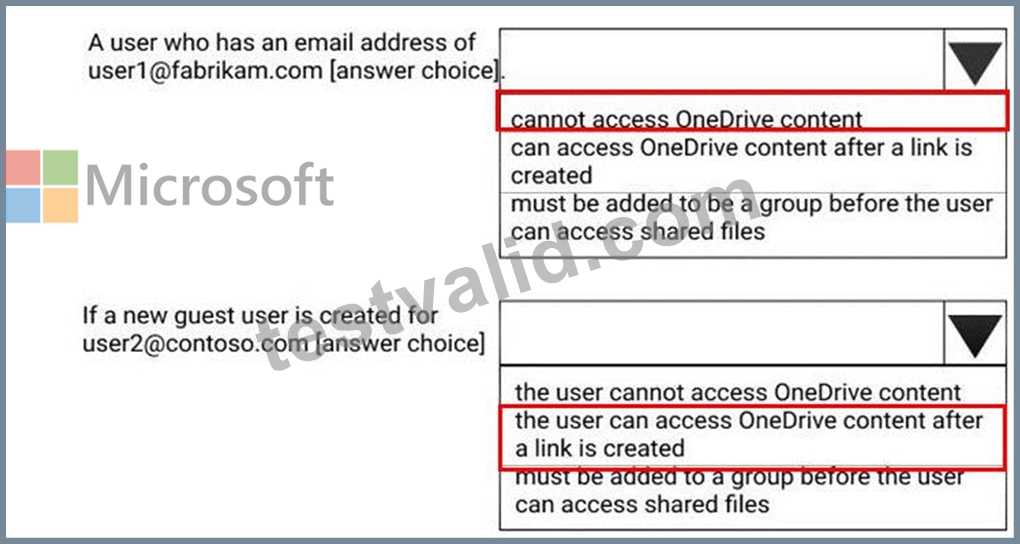
References:
https://docs.microsoft.com/en-us/onedrive/manage-sharing
NEW QUESTION 20
You need to create Group3.
What are two possible ways to create the group?
- A. a security group in the Microsoft 365 admin center
- B. an Office 365 group in the Microsoft 365 admin center
- C. a distribution list in the Microsoft 365 admin center
- D. a security group in the Azure AD admin center
- E. a mail-enabled security group in the Microsoft 365 admin center
Answer: B,C
Explanation:
Explanation/Reference:
Implement and manage identity and access
Testlet 3
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
The company has the offices shown in the following table.
Contoso has IT, human resources (HR), legal, marketing, and finance departments. Contoso uses Microsoft
365.
Existing Environment
Infrastructure
The network contains an Active Directory domain named contoso.com that is synced to a Microsoft Azure Active Directory (Azure AD) tenant. Password writeback is enabled.
The domain contains servers that run Windows Server 2016. The domain contains laptops and desktop computers that run Windows 10 Enterprise.
Each client computer has a single volume.
Each office connects to the Internet by using a NAT device. The offices have the IP addresses shown in the following table.
Named locations are defined in Azure AD as shown in the following table.
From the Multi-Factor Authentication page, an address space of 198.35.3.0/24 is defined in the trusted IPs list.
Azure Multi-Factor Authentication (MFA) is enabled for the users in the finance department.
The tenant contains the users shown in the following table.
The tenant contains the groups shown in the following table.
Customer Lockbox is enabled in Microsoft 365.
Microsoft Endpoint Manager Configuration
The devices enrolled in Microsoft Endpoint Manager are configured as shown in the following table.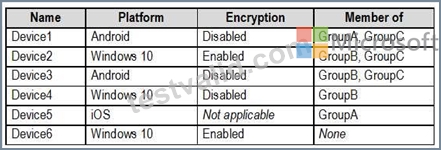
The device compliance policies in Microsoft Endpoint Manager are configured as shown in the following table.
The device compliance policies have the assignments shown in the following table.
The Mark devices with no compliance policy assigned as setting is set to Compliant.
Requirements
Technical Requirements
Contoso identifies the following technical requirements:
* Use the principle of least privilege
* Enable User1 to assign the Reports reader role to users
* Ensure that User6 approves Customer Lockbox requests as quickly as possible
* Ensure that User9 can enable and configure Azure AD Privileged Identity Management
NEW QUESTION 21
You have a hybrid Microsoft 365 environment. All computers run Windows 10 and are managed by using Microsoft Intune.
You need to create a Microsoft Azure Active Directory (Azure AD) conditional access policy that will allow only Windows 10 computers marked as compliant to establish a VPN connection to the on-premises network.
What should you do first?
- A. Enable Application Proxy in Azure AD
- B. From Active Directory Administrative Center, create a Dynamic Access Control policy
- C. From the Azure Active Directory admin center, create a new certificate
- D. From the Azure Active Directory admin center, configure authentication methods
Answer: C
Explanation:
Explanation/Reference:
Reference:
https://docs.microsoft.com/en-us/windows-server/remote/remote-access/vpn/ad-ca-vpn-connectivity- windows10
NEW QUESTION 22
You have the Microsoft conditions shown in the following table.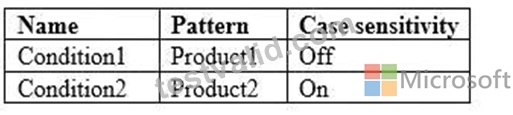
You have the Azure Information Protection labels shown in the following table.
You have the Azure Information Protection policies shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.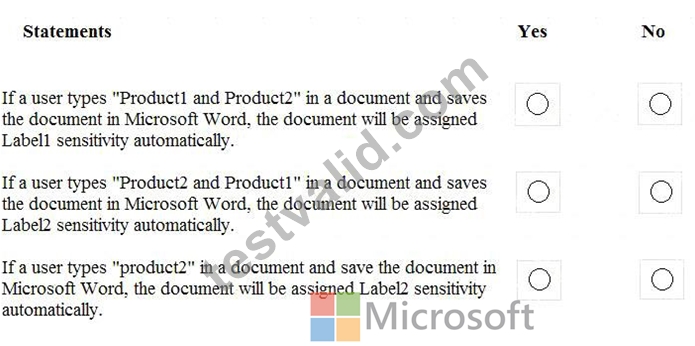
Answer:
Explanation: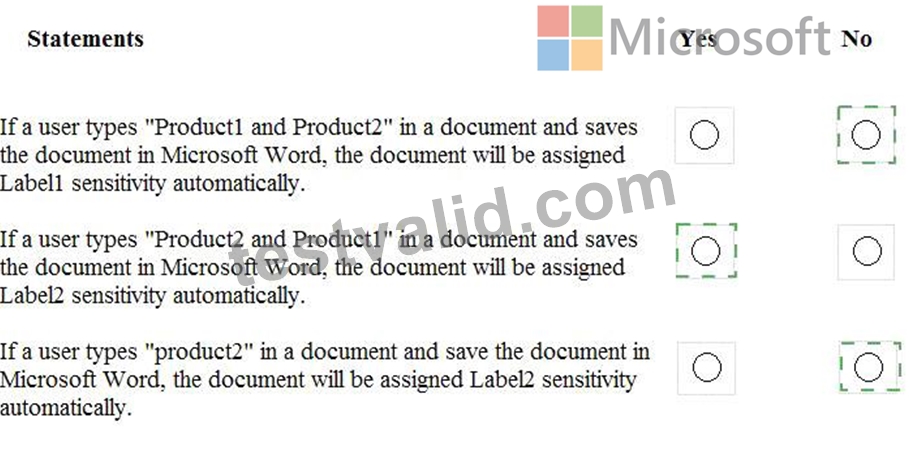
Explanation
NEW QUESTION 23
You have a Microsoft 365 subscription that contains 1,000 user mailboxes.
An administrator named Admin1 must be able to search for the name of a competing company in the mailbox of a user named User5.
You need to ensure that Admin1 can search the mailbox of User5 successfully. The solution must prevent Admin1 from sending User5.
Solution: You start a message trace, and then create a Data Subject request (DSR) case.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/exchange/policy-and-compliance/ediscovery/ediscovery?view=exchserver-2019
NEW QUESTION 24
Your network contains an on-premises Active Directory domain. The domain contains servers that run Windows Server and have advanced auditing enabled.
The security logs of the servers are collected by using a third-party SIEM solution.
You purchase a Microsoft 365 subscription and plan to deploy Azure Advanced Threat Protection (ATP) by using standalone sensors.
You need to ensure that you can detect when sensitive groups are modified and when malicious services are created.
What should you do?
- A. Turn on Delayed updates for the Azure ATP sensors.
- B. Configure auditing in the Office 365 Security & Compliance center.
- C. Enable the Audit account management Group Policy setting for the servers.
- D. Configure Event Forwarding on the domain controllers.
Answer: D
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/azure-advanced-threat-protection/configure-event-forwarding
NEW QUESTION 25
You have a Microsoft 365 subscription.
You create a retention policy and apply the policy to Exchange Online mailboxes.
You need to ensure that the retention policy tags can be assigned to mailbox items as soon as possible.
What should you do?
- A. From Exchange Online PowerShell, run Start-ManagedFolderAssistant
- B. From the Security & Compliance admin center, create a data loss prevention (DLP) policy
- C. From the Security & Compliance admin center, create a label policy
- D. From Exchange Online PowerShell, run Start-RetentionAutoTagLearning
Answer: C
Explanation:
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/labels
NEW QUESTION 26
You configure several Advanced Threat Protection (ATP) policies in a Microsoft 365 subscription.
You need to allow a user named User1 to view ATP reports in the Threat management dashboard.
Which role provides User1with the required role permissions?
- A. Information Protection administrator
- B. Service administrator
- C. Compliance administrator
- D. Security reader
- E. Message center reader
Answer: D
Explanation:
Explanation/Reference:
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/view-reports-for-atp#what-permissions-are- needed-to-view-the-atp-reports
NEW QUESTION 27
You have a Microsoft 365 subscription.
You need to include a custom sensitive information type in Data Subject Request (DSR) cases.
Which four actions should you perform in sequence? To answer, move the appropriate actions from thelist of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation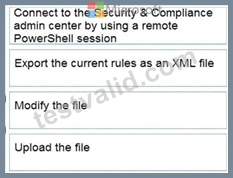
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/customize-a-built-in-sensitive-information-type?vie
NEW QUESTION 28
Your company has a Microsoft 365 subscription that contains the users shown in the following table.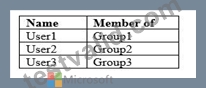
The company implements Windows Defender Advanced Threat Protection (Windows Defender ATP). Windows Defender ATP includes the roles shown in the following table: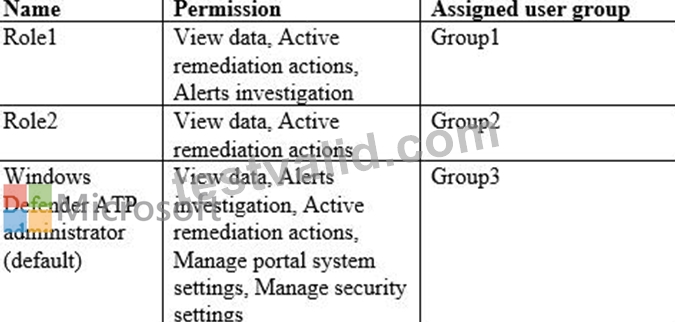
Windows Defender ATP contains the machine groups shown in the following table: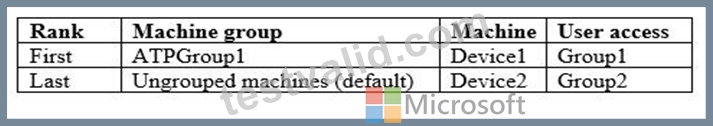
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.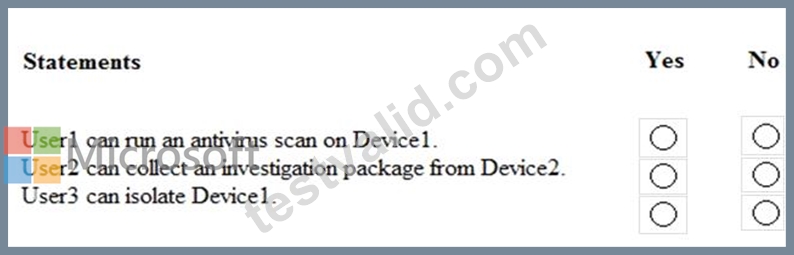
Answer:
Explanation: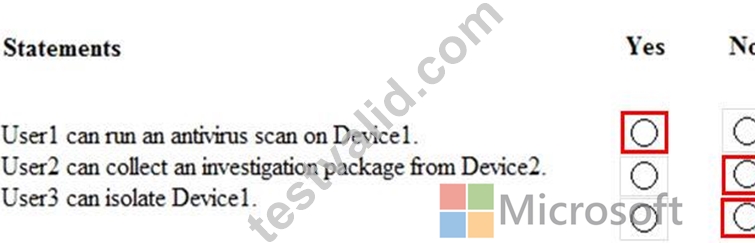
NEW QUESTION 29
Your network contains an on-premises Active Directory domain named contoso.com. The domain contains the groups shown in the following table.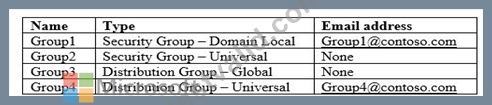
The domain is synced to a Microsoft Azure Active Directory (Azure AD) tenant that contains the groups shown in the following table.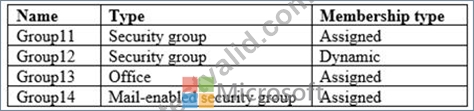
You create an Azure Information Protection policy named Policy1.
You need to apply Policy1.
To which groups can you apply Policy1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.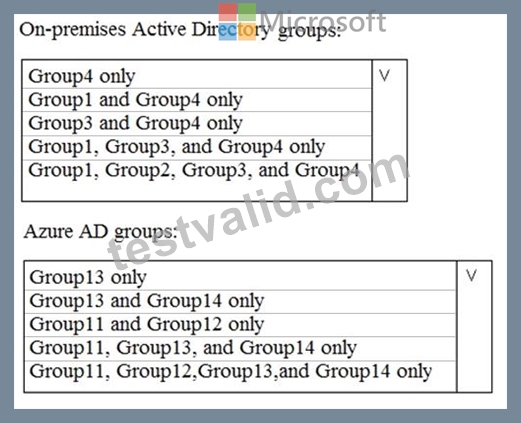
Answer:
Explanation: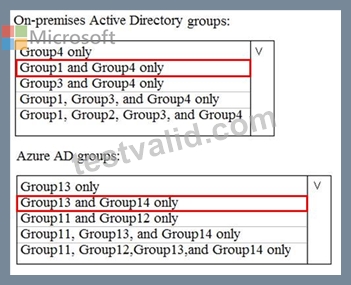
Reference:
https://docs.microsoft.com/en-us/azure/information-protection/prepare
NEW QUESTION 30
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some questions sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an on-premises Active Directory domain named contoso.com.
You install and run Azure AD Connect on a server named Server1 that runs Windows Server.
You need to view Azure AD Connect events.
You use the Application event log on Server1.
Does that meet the goal?
- A. No
- B. Yes
Answer: B
Explanation:
Explanation
References:
https://support.pingidentity.com/s/article/PingOne-How-to-troubleshoot-an-AD-Connect-Instance
NEW QUESTION 31
You plan to add a file named ConfidentialHR.docx to a Microsoft SharePoint library.
You need to ensure that a user named Megan Bowen is notified when another user accesses ConfidentialHR.xlsx.
To complete this task, sign in to the Microsoft 365 portal.
Answer:
Explanation:
See explanation below.
Explanation
You need to configure an alert policy.
* Go to the Security & Compliance Admin Center.
* Navigate to Alerts > Alert Policies.
* Click on + New alert policy to create a new policy.
* Give the policy a name and select a severity level. For example: Medium.
* In the Category section, select Information Governance and click Next.
* In the Select an activity section, select Any file or folder activity.
* Click Add a condition and select File name.
* Type in the filename ConfidentialHR.xlsx and click Next.
* In the email recipients section, add Megan Bowen and click
* Click Finish to create the alert policy.
NEW QUESTION 32
Your network contains an on-premises Active Directory domain. The domain contains the servers shown in the following table.
You plan to implement Azure Advanced Threat Protection (ATP) for the domain.
You install an Azure ATP standalone sensor on Server1.
You need to monitor the domain by using Azure ATP.
What should you do?
- A. Configure port mirroring for DC1.
- B. Install the Microsoft Monitoring Agent on DC1.
- C. Install the Microsoft Monitoring Agent on Server!.
- D. Configure port mirroring for Server 1.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure-advanced-threat-protection/configure-port-mirroring
NEW QUESTION 33
Which IP address space should you include in the MFA configuration?
- A. 192.168.16.0/20
- B. 172.16.0.0/24
- C. 131.107.83.0/28
- D. 192.168.0.0/20
Answer: A
NEW QUESTION 34
You have a Microsoft 365 subscription that contains 1,000 user mailboxes.
An administrator named Admin1 must be able to search for the name of a competing company in the mailbox of a user named User5.
You need to ensure that Admin1 can search the mailbox of User5 successfully. The solution must prevent Admin1 from sending User5.
Solution: You assign the eDiscovery Manager role to Admin1, and then create an eDiscovery case.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
Explanation:
References:
https://docs.microsoft.com/en-us/exchange/policy-and-compliance/ediscovery/ediscovery?view=exchserver-2019
NEW QUESTION 35
......
Test Engine to Practice MS-500 Test Questions: https://www.testvalid.com/MS-500-exam-collection.html
Use Valid MS-500 Exam - Actual Exam Question & Answer: https://drive.google.com/open?id=1zd4UGRPzmBPWuOIsZjRsg6A56DrGqX5A