


About our ISO-IEC-27001-Lead-Auditor valid dumps
Our ISO-IEC-27001-Lead-Auditor valid dumps are created by a team of professional IT experts and certified trainers who focus on the study of ISO-IEC-27001-Lead-Auditor actual test for a long time. We constantly keep the updating of ISO-IEC-27001-Lead-Auditor valid vce to ensure every candidate prepare the PECB Certified ISO/IEC 27001 Lead Auditor exam practice test smoothly. Before you decide to buy our products, you can download the free demo of ISO-IEC-27001-Lead-Auditor test questions to check the accuracy of our dumps. Two weeks preparation prior to attend exam is highly recommended.
Online test engine
Online version is the best choice for IT workers because it is a simulation of ISO-IEC-27001-Lead-Auditor actual test and makes your exam preparation process smooth. It can support Windows/Mac/Android/iOS operating systems, which means you can do your ISO 27001 practice test on any electronic equipment. Besides, there is no limitation of the number of you installed. So you can practice ISO-IEC-27001-Lead-Auditor test questions without limit of time and location.
Our website is a leading dumps provider worldwide that offers the latest valid test questions and answers for certification test, especially for PECB actual test. We paid great attention to the study of ISO-IEC-27001-Lead-Auditor valid dumps for many years and are specialized in the questions of PECB Certified ISO/IEC 27001 Lead Auditor exam actual test. You can find everything that you need to pass test in our ISO-IEC-27001-Lead-Auditor valid vce. We not only provide you with valid ISO-IEC-27001-Lead-Auditor test questions and detailed ISO-IEC-27001-Lead-Auditor test answers , but also offer the most comprehensive service to you. That's why so many people choose to buy ISO 27001 valid dumps on our website. Our target is best quality products, best service, best pass rate.

Most effective and direct way for passing ISO-IEC-27001-Lead-Auditor actual test
Some people tend to choose training institution or online training to prepare their ISO-IEC-27001-Lead-Auditor actual test, which is expensive and time-consuming for most office workers. Comparing to attending classes, ISO-IEC-27001-Lead-Auditor valid dumps provided by our website can not only save your money and time, but also ensure you pass PECB actual test with high rate. You just need to spend your spare time to practice ISO-IEC-27001-Lead-Auditor test questions and remember ISO-IEC-27001-Lead-Auditor test answers skillfully; your pass rate is 100%.
PECB ISO-IEC-27001-Lead-Auditor Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
Reference: https://pecb.com/pdf/candidate-handbooks/pecb-candidate-handbook-iso-27001-lead-auditor-mc.pdf
No Help, Full Refund
We promise you pass ISO-IEC-27001-Lead-Auditor actual test with high pass rate. But if you failed the exam with our ISO-IEC-27001-Lead-Auditor valid vce, we guarantee full refund. Or you can choose to wait the updating or free change to other dumps if you have other test.
Instant Download ISO-IEC-27001-Lead-Auditor Exam Braindumps: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
One-year free update ISO-IEC-27001-Lead-Auditor valid vce
Once you bought ISO-IEC-27001-Lead-Auditor valid dumps from our website, you will be allowed to free update your ISO-IEC-27001-Lead-Auditor test questions one-year. If there is latest version released, we will send the updated ISO-IEC-27001-Lead-Auditor valid dumps to your email immediately.
PECB Certified ISO/IEC 27001 Lead Auditor Sample Questions:
You are carrying out your first third-party ISMS surveillance audit as an Audit Team Leader. You are presently in the auditee's data centre with another member of your audit team.
You are currently in a large room that is subdivided into several smaller rooms, each of which has a numeric combination lock and swipe card reader on the door. You notice two external contractors using a swipe card and combination number provided by the centre's reception desk to gain access to a client's suite to carry out authorised electrical repairs.
You go to reception and ask to see the door access record for the client's suite. This indicates only one card was swiped. You ask the receptionist and they reply, "yes it's a common problem. We ask everyone to swipe their cards but with contractors especially, one tends to swipe and the rest simply 'tailgate' their way in" but we know who they are from the reception sign-in.
Based on the scenario above which one of the following actions would you now take?
- A. Raise a nonconformity against control A.7.6 'working in secure areas' as security measures for working in secure areas have not been defined
- B. Take no action. Irrespective of any recommendations, contractors will always act in this way
- C. Raise an opportunity for improvement to have a large sign in reception reminding everyone requiring access must use their swipe card at all times
- D. Raise a nonconformity against control A.5.20 'addressing information security in supplier relationships' as information security requirements have not been agreed upon with the supplier
- E. Raise a nonconformity against control A.7.2 'physical entry' as a secure area is not adequately protected
- F. Determine whether any additional effective arrangements are in place to verify individual access to secure areas e.g. CCTV
- G. Raise an opportunity for improvement that contractors must be accompanied at all times when accessing secure facilities
- H. Tell the organisation they must write to their contractors, reminding them of the need to use access cards appropriately
Correct Answer: E 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
Select the correct sequence for the information security risk assessment process in an ISMS.
To complete the sequence click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the options to the appropriate blank
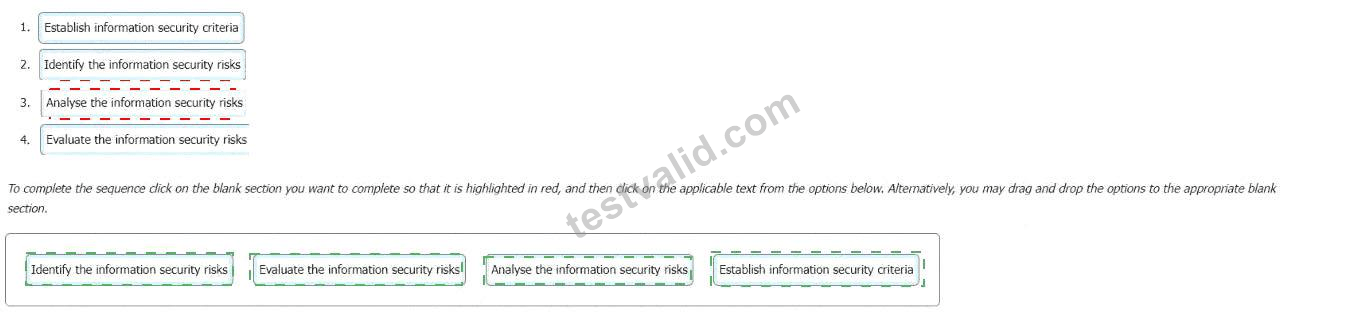
Correct Answer:
Explanation: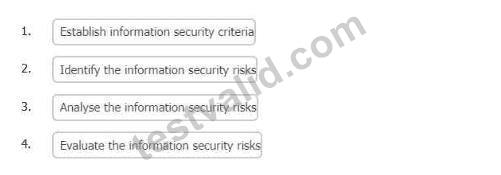
According to ISO 27001:2022, the standard for information security management systems (ISMS), the correct sequence for the information security risk assessment process is as follows:
* Establish information security criteria
* Identify the information security risks
* Analyse the information security risks
* Evaluate the information security risks
The first step is to establish the information security criteria, which include the risk assessment methodology, the risk acceptance criteria, and the risk evaluation criteria. These criteria define how the organization will perform the risk assessment, what level of risk is acceptable, and how the risks will be compared and prioritized.
The second step is to identify the information security risks, which involve identifying the assets, threats, vulnerabilities, and existing controls that are relevant to the ISMS. The organization should also identify the potential consequences and likelihood of each risk scenario.
The third step is to analyse the information security risks, which involve estimating the level of risk for each risk scenario based on the criteria established in the first step. The organization should also consider the sources of uncertainty and the confidence level of the risk estimation.
The fourth step is to evaluate the information security risks, which involve comparing the estimated risk levels with the risk acceptance criteria and determining whether the risks are acceptable or need treatment.
The organization should also prioritize the risks based on the risk evaluation criteria and the objectives of the ISMS.
References: ISO 27001:2022 Clause 6.1.2 Information security risk assessment, ISO 27001 Risk Assessment
& Risk Treatment: The Complete Guide - Advisera, ISO 27001 Risk Assessment: 7 Step Guide - IT Governance UK Blog
Scenario 6
Sinvestment is an insurance provider that offers a wide range of coverage options, including home, commercial, and life insurance. Originally established in North California, the company has expanded its operations to other locations, including Europe and Africa. In addition to its growth, Sinvestment is committed to complying with laws and regulations applicable to its industry and preventing any information security incident. They have implemented an information security management system (ISMS) based on ISO
/IEC 27001 and have applied for certification.
A team of auditors was assigned by the certification body to conduct the audit. After signing a confidentiality agreement with Sinvestment, they started the audit activities. For the activities of the stage 1 audit, it was decided that they would be performed on site, except the review of documented information, which took place remotely, as requested by Sinvestment.
The audit team started the stage 1 audit by reviewing the documentation required, including the declaration of the ISMS scope, information security policies, and internal audit reports. The evaluation of the documented information was based on the content and procedure for managing the documented information.
In addition, the auditors found out that the documentation related to information security training and awareness programs was incomplete and lacked essential details. When asked, Sinvestment's top management stated that the company has provided information security training sessions to all employees.
The stage 2 audit was conducted three weeks after the stage 1 audit. The audit team observed that the marketing department (not included in the audit scope) had no procedures to control employees' access rights.
Since controlling employees' access rights is one of the ISO/IEC 27001 requirements and was included in the company's information security policy, the issue was included in the audit report.
Question
Was Sinvestment's request for reviewing documented information remotely acceptable?
- A. Yes, documented information can be reviewed remotely.
- B. No, as the combination of different locations can negatively impact the audit efficiency.
- C. No, as it can lead to a breach of confidentiality.
Correct Answer: A 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
Correct Answer:
Explanation:
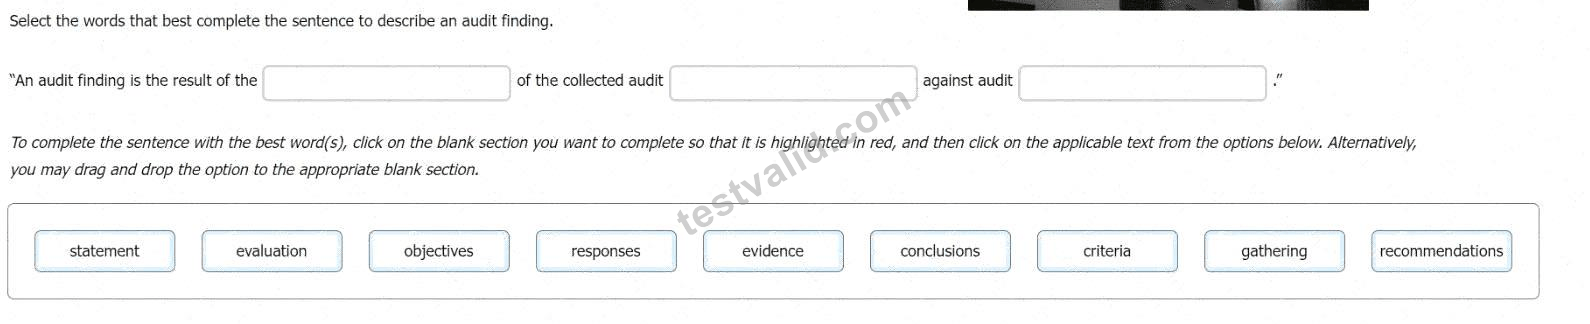
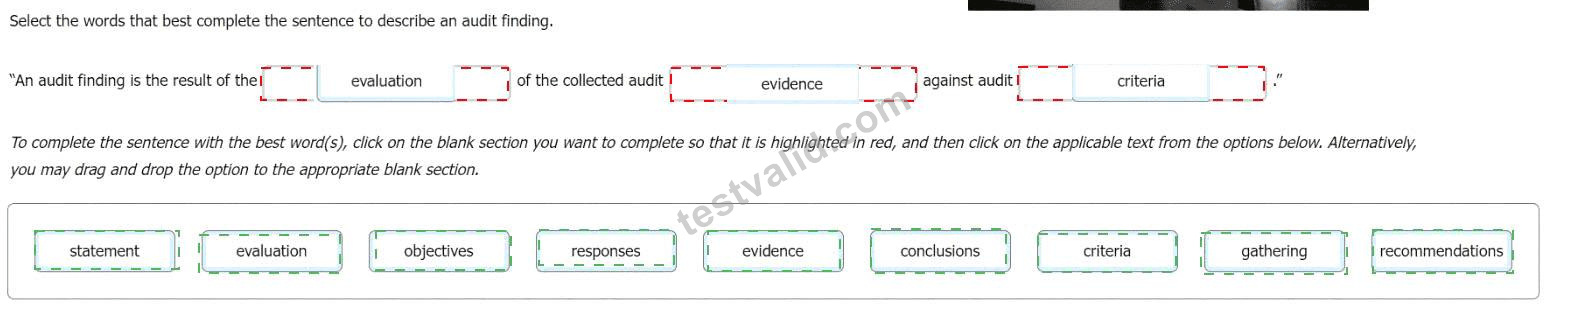
An audit finding is the result of the evaluation of the collected audit evidence against audit criteria.
Scenario 5: Cobt. an insurance company in London, offers various commercial, industrial, and life insurance solutions. In recent years, the number of Cobt's clients has increased enormously. Having a huge amount of data to process, the company decided that certifying against ISO/IEC 27001 would bring many benefits to securing information and show its commitment to continual improvement. While the company was well- versed in conducting regular risk assessments, implementing an ISMS brought major changes to its daily operations. During the risk assessment process, a risk was identified where significant defects occurred without being detected or prevented by the organizations internal control mechanisms.
The company followed a methodology to implement the ISMS and had an operational ISMS in place after only a few months After successfully implementing the ISMS, Cobt applied for ISO/IEC 27001 certification Sarah, an experienced auditor, was assigned to the audit Upon thoroughly analyzing the audit offer, Sarah accepted her responsibilities as an audit team leader and immediately started to obtain general information about Cobt She established the audit criteria and objective, planned the audit, and assigned the audit team members' responsibilities.
Sarah acknowledged that although Cobt has expanded significantly by offering diverse commercial and insurance solutions, it still relies on some manual processes Therefore, her initial focus was to gather information on how the company manages its information security risks Sarah contacted Cobt's representatives to request access to information related to risk management for the off-site review, as initially agreed upon for part of the audit However, Cobt later refused, claiming that such information is too sensitive to be accessed outside of the company This refusal raised concerns about the audit's feasibility, particularly regarding the availability and cooperation of the auditee and access to evidence Moreover, Cobt raised concerns about the audit schedule, stating that it does not properly reflect the recent changes the company made It pointed out that the actions to be performed during the audit apply only to the initial scope and do not encompass the latest changes made in the audit scope Sarah also evaluated the materiality of the situation, considering the significance of the information denied for the audit objectives. In this case, the refusal by Cobt raised questions about the completeness of the audit and its ability to provide reasonable assurance. Following these situations, Sarah decided to withdraw from the audit before a certification agreement was signed and communicated her decision to Cobt and the certification body. This decision was made to ensure adherence to audit principles and maintain transparency, highlighting her commitment to consistently upholding these principles.
Based on the scenario above, answer the following question:
Question:
Based on the role of Sarah described in Scenario 5, which of the following should NOT be part of her responsibilities?
- A. Assigning responsibilities to the audit team members
- B. Defining the audit criteria and objectives
- C. Planning the audit
Correct Answer: A 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
Viewing page 1 out of 84 pages.
Viewing questions 1-5 out of 418 questions.

 868 Customer Reviews


